On this page
Cloud Organization Device Groups
Overview
Cloud organization device groups are a type of device group in TOS that lets you manage cloud accounts at the organizational level rather than individually.
Configure cloud organizations to automatically discover and onboard accounts, eliminating the need to manually import each new account. Define the authentication credentials once for the organization and reuse them for any account you associate with the organization.
The Cloud Organizations page in Device Groups lists existing organizations, their settings, and options available to manage them.
Cloud Organizations page reference
Below is an example of the Cloud Organizations page.
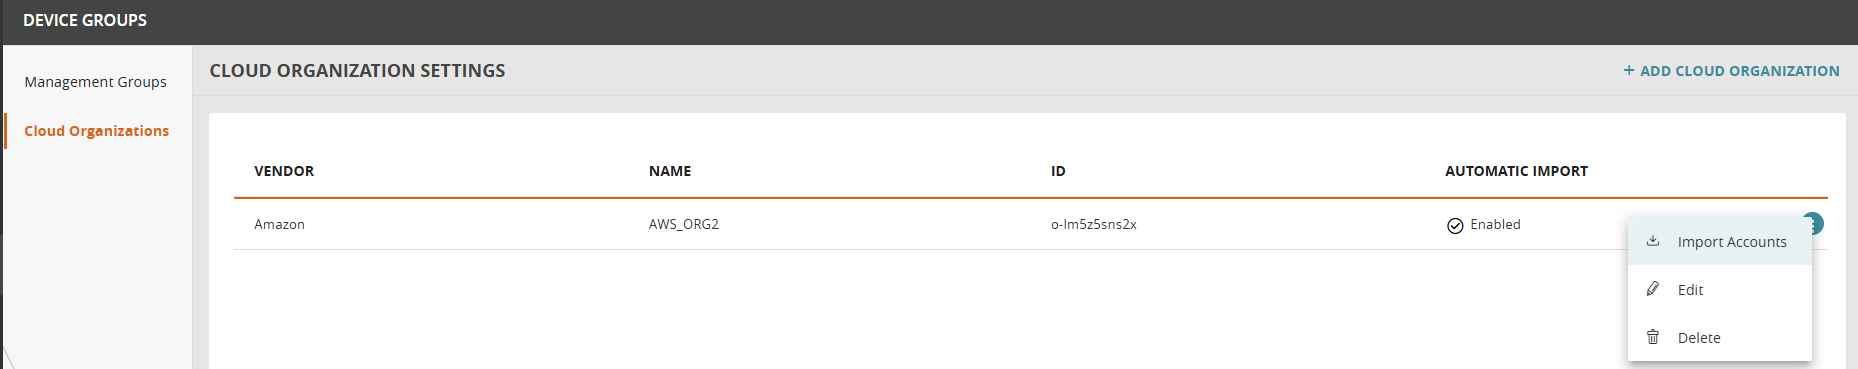
The table describes the information displayed and the actions available for a cloud organization.
|
Item |
Description |
|---|---|
|
Vendor |
The cloud provider hosting the cloud organization. |
|
Name |
The name assigned to the cloud organization. |
|
ID |
The unique identifier representing the cloud organization and its member accounts. Differs according to the vendor. |
|
Hierarchy |
The level in the cloud provider's hierarchy that the cloud organization is mapped to. The level is different for each vendor. In AWS, for example, it is an organizational unit (OU), and in Azure, it is a management group. |
|
Automatic Import |
Indicates if automatic account import is enabled or disabled for the cloud organization. |
|
Domain |
The default domain, or in a multi-domain environment, the specific domain from which the accounts are imported. |
|
Last Run |
The date and time of the most recent automatic or manual account import. |
Adding cloud organizations
Clicking Add Cloud Organization lets you add a cloud organization by configuring the organization settings, including credentials and settings for automatic account import:
Managing cloud organizations
To manage a cloud organization, select it and choose an option from the context menu.
-
In SecureTrack, go to Monitoring > Device Groups > Cloud Organizations.
-
Select an organization and choose an option from the context menu: Import Accounts, Edit, Delete.
Manually import accounts
Manually import member accounts or subscriptions for cloud organizations when needed, regardless of whether you have enabled automatic import of the same. Manual import behavior depends on whether automatic import is enabled for the cloud organization.
In large cloud environments, the volume of entities can increase the duration of manual imports and impact performance.
Manual import behavior
When you manually import accounts:
-
If automatic import is enabled, the member accounts or subscriptions are imported based on the settings configured for automatic import.
-
If automatic import is disabled, the member accounts or subscriptions are imported into the default domain in TOS.
Other import settings
These import settings are enabled by default :
-
Collect traffic logs for rule usage analysis
-
Enable topology
-
Automatic VPC/VNet Import
Edit cloud organization settings
Update cloud organization settings, including automatic account import settings. Changes affect only newly imported accounts; existing accounts are not affected.
Delete cloud organization
Remove the cloud organization from SecureTrack. Accounts previously associated with the organization retain the credentials last defined in the organization's settings for authentication.
Related topics
Was this helpful?
Thank you!
We’d love your feedback
We really appreciate your feedback
Send this page to a colleague